 Skip to content


The bar for cybersecurity email marketing is higher than ever.
Security buyers do more private research, mailbox providers enforce stricter sender rules, and your ICP has less patience for generic “thought leadership.” That means cybersecurity email demand generation needs tighter targeting, stronger deliverability hygiene, and offers that earn attention from skeptical technical audiences.
This guide is written for experienced B2B tech and SaaS marketers. It’s focused on what to do this quarter: how to build lists you can stand behind, how to design emails that generate real engagement signals, and how to evaluate partners without getting distracted by vanity metrics.
Why cybersecurity email demand generation feels harder than it used to
Two things are happening at the same time. First, cybersecurity buyers increasingly complete meaningful evaluation outside of vendor-controlled channels. A buyer might show up “late,” after weeks of reading, asking peers, and quietly narrowing options. ISMG captures this dynamic well: by the time a buyer fills out a form, much of the decision work already happened elsewhere.
Second, inbox placement is less forgiving. Gmail’s bulk sender rules (5,000+ emails/day to Gmail addresses) require authentication (SPF, DKIM, DMARC), aligned “From” domains, and one-click unsubscribe for marketing messages.
If your program is underperforming, it’s usually not one big issue. It’s small compounding gaps: list quality, domain setup, unclear positioning, weak segmentation, or offers that don’t match the stage of research.
Start with deliverability: the unglamorous foundation that determines everything
Before you touch copy, make sure you can reliably land in the inbox. If your messages don’t arrive, nothing downstream matters.
Meet mailbox provider requirements (and assume they’ll get stricter)
At minimum, you should have SPF, DKIM, and DMARC configured correctly. Gmail explicitly recommends setting these up, and requires DMARC for high-volume senders, along with alignment between the “From” domain and SPF or DKIM domain.
Microsoft documentation also explains how SPF, DKIM, and DMARC work together and calls out the importance of aligning the “From” domain with what passes authentication, especially when using third-party senders.
If you want a neutral security-oriented reference point, NIST’s “Trustworthy Email” publication covers email security mechanisms, including SPF, DKIM, DMARC, and TLS.
Operational checks experienced teams don’t skip
- Use a dedicated sending subdomain for outbound and newsletters so that you can protect your primary domain’s reputation.
- Keep your “From” identity consistent. Security audiences notice brand spoofing risk and inconsistency fast.
- Implement one-click unsubscribe properly (header + visible link), and process unsubscribes quickly. Gmail has been explicit here.
- Watch spam complaint rate like a hawk. Gmail’s sender guidelines FAQ discusses spam-rate thresholds and eligibility behaviors.
Deliverability is not a “set it and forget it” project. It’s a living system that gets better with consistent list hygiene, stable volume patterns, and content people actually want.
Define the cybersecurity email demand generation job to be done
If you’re trying to do everything in one email motion, you’ll end up doing nothing well.
For cybersecurity, the most reliable email outcomes tend to be earlier-journey and research-aligned: getting the right people to engage, building recognition, and generating signals that your audience is in-category and paying attention.
Pick 1–2 primary signals per motion
Here are examples of signals that map well to cybersecurity buying behavior:
- Repeat site visits to high-intent pages (integration pages, security/compliance docs, pricing architecture, migration guides).
- Content depth signals (time on page, scroll depth, second-asset consumption).
- Newsletter engagement over time (steady clicks are more meaningful than opens in a post-Apple MPP world).
- Topic-level engagement (e.g., identity, email security, cloud posture, data security) that helps you confirm ICP fit.
Note on metrics: open rates are directional, not definitive. Industry benchmarks still report open rates, but clicks are a better “did this matter” indicator. For context, DMA’s Email Benchmarking Report 2025 cites an average open rate of 35.9% and a unique click rate of 2.3%.
Segmentation that actually works in cybersecurity (and doesn’t explode your workload)
You don’t need 25 segments. You need a few that reflect real differences in pain, language, and proof requirements.
Segment by “security problem + environment,” not just industry
Industry matters. But in cybersecurity, the environment and control surface often matter more for email relevance.
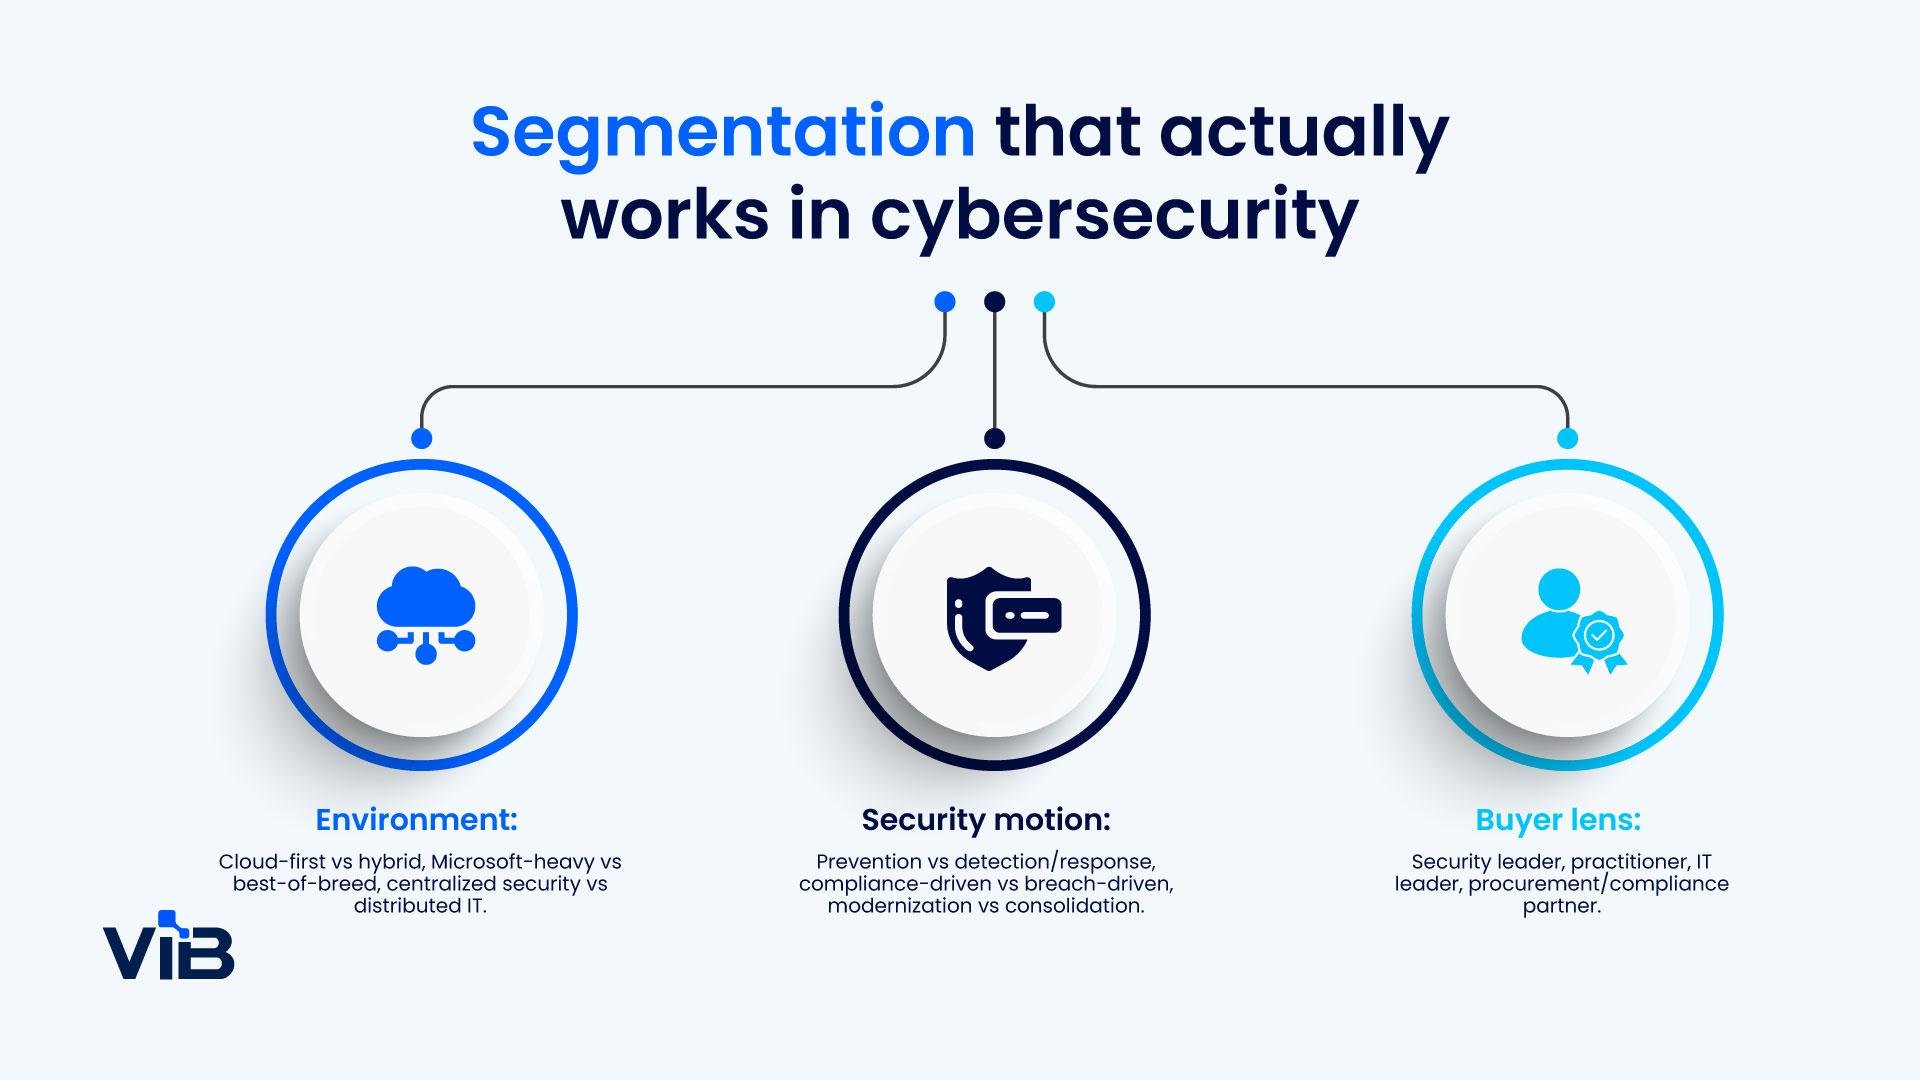
- Environment: cloud-first vs hybrid, Microsoft-heavy vs best-of-breed, centralized security vs distributed IT.
- Security motion: prevention vs detection/response, compliance-driven vs breach-driven, modernization vs consolidation.
- Buyer lens: security leader, practitioner, IT leader, procurement/compliance partner.
Use “proof style” as a segmentation lever
Different audiences need different proof. A security engineer might want technical depth and config clarity. A CISO might want risk framing and operational outcomes. A compliance stakeholder might want mappings and audit readiness.
When your email offer matches the proof style the reader prefers, you’ll see more consistent engagement signals, even with smaller lists.
Offers that get clicks from security audiences (without being gimmicky)
Security buyers are busy and skeptical. Your offer has to respect that.
High-performing offer types for cybersecurity email programs
- Threat brief or monthly digest: concise, repeatable, and easy to subscribe to.
- Practical implementation guides: “how to roll out X safely,” “common misconfigurations,” “what to monitor.” NIST’s “Trustworthy Email” and mailbox provider guidance can be helpful anchors for email security topics.
- Evaluation checklists: what to ask vendors, what to verify in a trial, what evidence to request.
- Security/compliance explainers: SOC 2, ISO 27001, FedRAMP context, logging expectations, data residency, etc.
One copy rule that matters more than “best practices”
Make the reader feel like you understand their environment in the first two lines.
In cybersecurity email demand generation, relevance beats cleverness. “Microsoft-heavy identity teams” or “cloud security teams managing CSPM tool sprawl” is better than generic persona language.
Email content design: what experienced marketers should optimize for now
Most teams overthink templates and underthink reading experience.
Write like a peer, not a brand
Security audiences can smell marketing distance. Keep it human and specific. Use short paragraphs, clear nouns, and verbs that say what changes for the reader.
A simple structure works well:
- Context: what changed in the world or in the buyer’s environment.
- Point of view: your take, in plain English.
- Proof: link to a practical asset or third-party anchor.
- Next step: one focused CTA (read, download, compare, or reply).
Keep CTAs single-threaded
If your email asks the reader to read a guide, don’t also ask them to watch a webinar, check out a product page, and book time. Pick the next best step for this segment at this stage.
Measure what you can act on
If you can’t change a metric with a specific lever, it’s a distraction.
- Inbox placement and bounce rate → fix domain setup, sending patterns, list hygiene.
- Click rate by segment → tighten offer-message match, change proof style, improve landing page continuity.
- Engaged account clusters → build follow-up paths that go deeper on the topic they touched.
Benchmarks can help you double-check. But your real goal is trend improvement inside your own program, by segment and topic.
Vendor and partner options for cybersecurity email demand generation
If your team is lean, partners can help you move faster. The key is choosing based on what you actually need: audience access, content production, campaign operations, or signal generation across accounts.
Option 1: Newsletter sponsorships and publisher programs (fast reach, variable intent)
Cybersecurity buyers do rely on third-party sources during research. TechnologyAdvice’s cybersecurity properties highlight ongoing newsletter audiences for IT and security professionals.
These programs can be useful for awareness and for testing which themes earn clicks. They’re less reliable for deep qualification unless you have a strong follow-up and segmentation plan once someone engages.
Option 2: Marketing automation + deliverability specialists (better hygiene, better sending)
If deliverability is the bottleneck, prioritize technical help first. Gmail’s bulk sender requirements and Microsoft’s authentication guidance give you a clear checklist, but implementation details still trip teams up.
Deliverability partners are especially valuable when you’re ramping volume, adding new sending domains, or migrating platforms.
Option 3: ViB Emails (campaign execution built around engagement signals and ICP fit)
ViB Emails is a practical option when you want to run consistent cybersecurity email demand generation programs without turning your team into a full-time email production studio.
The sweet spot is when you already have a point of view and a defined ICP, but you need help translating that into repeatable email motions that generate measurable engagement. That includes segmentation support, message testing, and content offers that match how security buyers actually research.
Done well, the output is simple: cleaner targeting, better deliverability hygiene, and more reliable engagement signals you can route into the rest of your go-to-market motion.

Conclusion: make your email program feel like part of the buyer’s research
The best cybersecurity email demand generation programs don’t feel like campaigns. They feel like helpful inputs to an ongoing evaluation.
Start with deliverability fundamentals and mailbox provider requirements. Then narrow your segmentation to a few meaningful cuts, choose offers that match proof expectations, and measure signals you can actually act on.
If you do those things consistently, email becomes a dependable way to stay present in the market, earn repeat attention from the right accounts, and learn what your ICP is leaning into right now.


