 Skip to content


Cybersecurity buyer intent data is harder to come by than most categories. Research cycles are noisy, buying groups are large, and “interest” often looks like student learning, partner enablement, or analyst research. The difference between useful intent and random activity comes down to two things: signal quality and how you operationalize it.
This guide is built for experienced B2B tech and SaaS marketers looking for trustworthy intent data sources, how those sources actually generate signals, and how to turn those signals into targeted programs that reach the right accounts before they’re already deep into a shortlist. It focuses on practical evaluation: where the data comes from, what you’ll actually get, and when each source tends to work best.
What “cybersecurity buyer intent data” really means in practice
Most teams use “intent” as shorthand for behavior that suggests an account is in an active research cycle. That’s the safe definition, and it’s the one you can plan around.
In cybersecurity, the most reliable programs usually combine multiple intent types, because any single feed can over-index on curiosity. Gartner reported that in its 2023 Technology Marketing Benchmarks Survey, 93% of technology marketers at $100M+ revenue used third-party intent data for at least one use case.
In other words, lots of teams buy intent. The teams that win are picky about the source and disciplined about activation.
Three intent “buckets” you should separate (even if vendors don’t)
When you evaluate cybersecurity buyer intent data sources, it helps to categorize them by where the signal originates. Different sources answer different questions.
- First-party intent: your own properties (website, product, trials, webinars you host, email engagement). Highest relevance, limited scale.
- Second-party intent: partner or publisher data shared directly with you (often through a platform). Good relevance, moderate scale, usually clearer provenance.
- Third-party intent: broader web consumption, co-ops, bidstream, and aggregated research behavior. Largest scale, but you need to validate relevance and timing carefully.
Once you separate these buckets, your tool choices get easier. You stop expecting third-party intent to do a first-party job.

The best sources of cybersecurity buyer intent data (and what each is good for)
Below are commonly used sources that show up in real B2B tech stacks. This isn’t a “top 10” list based on features. It’s a sourcing view: where the signals come from, what you can realistically do with them, and common pitfalls for cybersecurity teams.
1) Bombora (Company Surge) for topic-based third-party intent
Bombora is one of the best-known third-party intent providers. Their core concept is topic-based consumption analysis, packaged as Company Surge. Bombora emphasizes its topic taxonomy as the foundation of its intent measurement.
For cybersecurity, Bombora tends to be useful when you have a clear set of topic clusters (not just one keyword) and you want broad account coverage to guide targeting, segmentation, and content prioritization.
What it’s best for
- Building and refreshing account lists based on category research patterns
- Prioritizing paid media audiences and retargeting tiers by intent strength
- Informing content strategy by seeing what topics are trending in your ICP
What to watch for
In cybersecurity, broad topics (like “zero trust”) can be noisy. Ask how topics are defined, how they’re classified, and how often they’re refreshed. Bombora notes its intent topics are continuously updated as markets change.
Also validate whether you’re buying Bombora directly or via another platform that licenses the data. You may be paying for packaging rather than new signal.
2) Informa TechTarget Priority Engine for opt-in, tech research signals
If you market to IT and security teams, TechTarget is often on the shortlist because of its position in the tech research ecosystem. TechTarget describes Priority Engine as providing access to active in-market accounts and “fully permissioned prospects” doing purchase research in specific technology markets.
They also position Account Intent Feeds as being powered by first-party, buy-cycle content research.
What it’s best for
- Prioritizing accounts that are actively researching specific security categories
- Planning category campaigns around observed research behavior
- Aligning SDR and marketing touches around “what they’re researching” rather than generic messaging
What to watch for
Make sure your internal team can act on the data quickly. If your operational cadence is monthly, weekly research signals can go stale before you do anything with them.
3) G2 Buyer Intent for in-market comparison behavior
G2 intent is a different style of signal. Instead of inferring interest from broad content consumption, it’s tied to software discovery and evaluation behavior inside G2 properties. G2 positions Buyer Intent as a way to bring signals together so teams can find and connect with in-market accounts.
For cybersecurity companies competing in crowded categories, G2 can be valuable because it’s closer to “vendor comparison” than generic research.
What it’s best for
- Competitive conquesting and “category showdown” campaigns
- Retargeting and ad personalization based on category and product-page engagement
- Helping product marketing understand evaluation patterns and objections
What to watch for
If your category presence on G2 is weak (limited reviews, unclear positioning, poor category fit), your G2 intent signal may be lower volume than you expect. Treat it as a strong signal when it exists, not as your only source of truth.
4) 6sense for scoring, modeling, and blending multiple signals
6sense is often used as an orchestration layer, not just an “intent vendor.” In its documentation, 6sense describes intent scores as an output of a predictive company activity model, used to determine buying stages.
It also describes ingesting first-party and third-party intent data and using predictive models to produce ICP fit, buying stage, and persona engagement.
What it’s best for
- Turning multiple intent streams into a unified prioritization model
- Coordinating media, web personalization, and outbound sequencing by account stage
- Measuring engagement lift across target segments, not just lead volume
What to watch for
Model outputs can look authoritative even when the inputs are messy. Your best move is to run a short calibration period: pick a few cybersecurity segments, define the behaviors you care about, and validate whether the “hot accounts” match real-world engagement and fit.
5) Demandbase for account intelligence and intent at scale
Demandbase positions its intent approach as combining breadth and flexibility (including bidstream keywords) with curated content quality.
They also document practical details like retaining up to 13 months of historical intent data (depending on availability).
What it’s best for
- Account selection and prioritization for ABM programs
- Always-on audience building for cybersecurity categories with long research cycles
- Connecting intent to account intelligence workflows (ads, site personalization, routing)
What to watch for
In cybersecurity, “research” often spikes after incidents, audits, or leadership changes. If your program treats every spike as immediate buying intent, you’ll burn budget. Use historical context and firmographic fit checks before you escalate.
6) NetLine for permissioned, buyer-level content intent
If you want intent tied to actual content registrations, NetLine is worth a look. NetLine positions its platform as powered by first-party content registrations and includes buyer activity alerts.
This can be especially useful in cybersecurity, where a clear content trail (what they downloaded, when, and how) is often easier to operationalize than abstract topic spikes.
How to evaluate cybersecurity intent sources (a marketer’s checklist)
Most disappointment with cybersecurity buyer intent data comes from buying before defining what “good” looks like.
Here’s a practical set of questions that tends to separate strong sources from expensive dashboards.
Start with provenance and transparency
- Where does the signal originate? First-party research behavior, publisher co-op consumption, bidstream, review-site evaluation, content registrations, or modeled blends?
- Can you see the underlying activity? You don’t need every click, but you do need enough context to write relevant messaging.
- How is it classified? Topic taxonomy and classification methods matter, especially in security where adjacent topics overlap.
Then validate fit for cybersecurity buying patterns
Security intent works best when you plan for buying groups and long evaluation windows. Vendor docs that explicitly support that reality tend to be more operationally useful.
- Time horizon: Are you trying to influence early research, or capture active evaluation signals?
- Category precision: Can you map signals to sub-categories (e.g., EDR vs. XDR vs. MDR) without collapsing into generic “security”?
- Activation surface: Does the data land in the systems you use (CRM/MAP/ads) quickly enough to act?
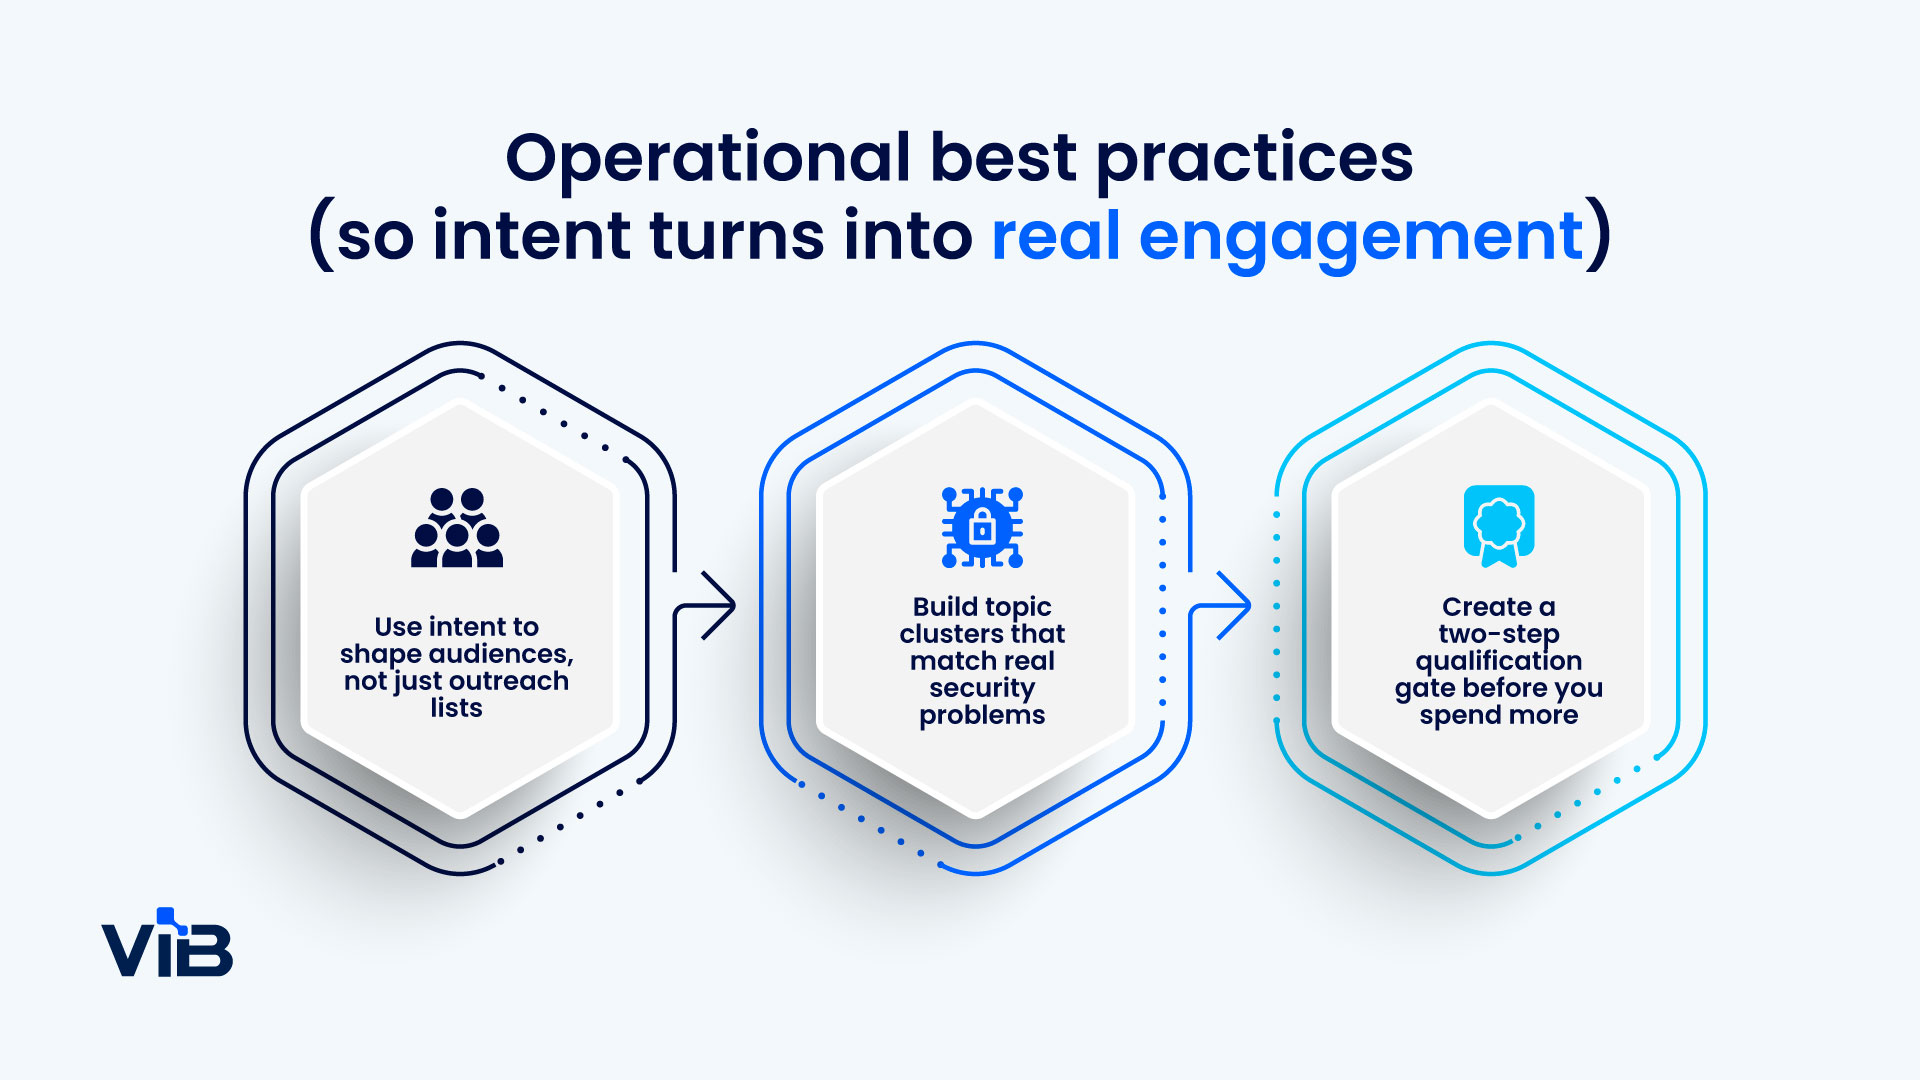
Operational best practices (so intent turns into real engagement)
Once you pick a cybersecurity buyer intent data source, the goal is to translate it into programs your team can run every week without heroics.
Use intent to shape audiences, not just outreach lists
The most consistent use case is paid media and retargeting. Intent helps you narrow from “everyone in cybersecurity” to “accounts showing category interest right now,” while still giving you room to educate before they raise their hand.
Build topic clusters that match real security problems
If you only target single keywords, you’ll chase noise. Clusters give you a better chance of separating “learning” from “evaluation.” This is especially true for big umbrella terms like zero trust, IAM, or ransomware preparedness.
Create a two-step qualification gate before you spend more
A simple way to reduce wasted effort is to require:
- Fit confirmation: firmographics/technographics align with your ICP.
- Second signal: web engagement, webinar attendance, a review-site visit, or another corroborating behavior.
This keeps intent from turning into broad, expensive targeting that looks strategic but performs like awareness.
Conclusion: better cybersecurity intent starts with better sourcing
The fastest way to improve results with cybersecurity buyer intent data isn’t buying more vendors. It’s choosing the right mix of sources for your motion, validating signal quality, and building a simple operating system your team can run every week.
Start with clarity on signal provenance and timing. Build topic clusters that reflect real security initiatives. Add a fit check and a second corroborating signal before you scale spend. Then choose the sources that match your goals.


